
How to Verify CASB Visibility Across Multiple Clouds
How can you verify a CASB’s visibility across multiple clouds? Start by defining the activity and data your security team needs to see, then generate a sample of that activity and trace it from the source system to the CASB. A connected status or a list of supported cloud providers is useful evidence of integration, but it does not establish that the right events, users, files, and administrative actions are visible.
A credible assessment compares the CASB’s observations with independent records from the cloud services in scope. It also tests the conditions that can create gaps: incomplete permissions, unmanaged devices, unsupported services, delayed ingestion, regional restrictions, and changes to accounts or integrations. The result should be a coverage record that states what was tested, what appeared, what did not, and what remains outside the test.
What should count as multicloud visibility?
Define visibility in terms of operational questions. Can an analyst identify who accessed a sensitive file, from which device, through which application, and what action followed? Can the team see a privileged change in a cloud account and connect it to the identity that made it? A CASB may answer some of these questions well while relying on other tools for the rest.
Begin with an inventory of the environment to be assessed: cloud providers, accounts or subscriptions, organizational tenants, sanctioned SaaS applications, and relevant users. Include separate business units and acquired environments where they fall within the intended deployment. Identify the events and data objects that matter for each service, rather than assuming that the same categories are available everywhere.
For a collaboration application, the priority may be file sharing, external access, downloads, and changes to sharing permissions. For an infrastructure cloud, it may be administrative activity, access to storage, and configuration changes. Some infrastructure and workload visibility may be better provided by cloud-native logs or other security tools; a CASB should be assessed against its intended role, not assumed to cover every cloud control.
Turn the inventory into a coverage matrix. Each row should describe a specific combination of service, account or tenant, activity, and required context. Record the expected source of evidence alongside the CASB integration method and the team responsible for reviewing it.
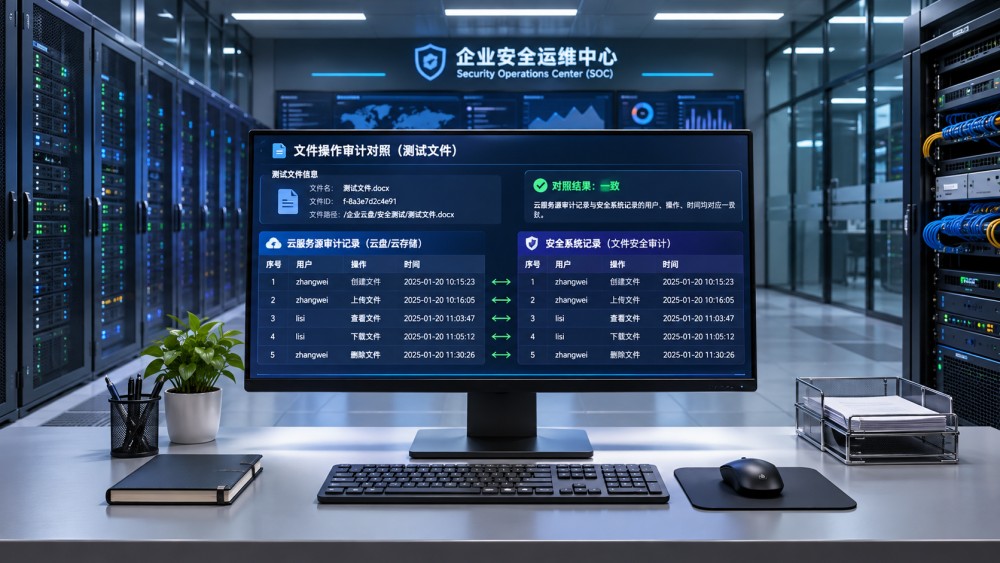
The matrix is also where exclusions become visible. A service that is outside the CASB’s intended scope is different from a service that should be covered but is missing because an integration is incomplete. Both matter, but they call for different decisions.
How do API and traffic-based integrations affect what you see?
Ask which collection path supplies each required observation. A CASB may use application or cloud-provider APIs, a proxy or other traffic-based control, log ingestion, or a combination. These paths see different parts of the environment and have different failure modes.
API integrations can provide access to activities and data exposed by a service, including some events that occur without traffic passing through a corporate network. Their scope depends on the provider’s available interfaces, the permissions granted, tenant configuration, licensing, and the CASB’s implementation. A successful connection does not prove that every relevant event type or account has been enabled.
Traffic-based visibility depends on the traffic actually reaching the inspection point and on what the product can inspect under the configured conditions. A managed laptop routed through an enforcement path may produce a different view from an unmanaged device, a mobile application, or a direct connection that bypasses that path. Encryption, application behavior, privacy settings, and inspection exceptions can further limit the content or context available.
For each high-priority use case, document the path from the user or service to the application and from the application to the CASB. Identify where a bypass is possible and whether an alternative source can cover it. If a CASB discovers applications from network logs, for example, that discovery reflects the traffic present in those logs; it does not by itself establish a complete inventory of all cloud use.
How should a team run a meaningful visibility test?
Select a manageable set of representative services and accounts, then expand once the method works. Include at least one high-value workflow per cloud or tenant in scope, plus conditions likely to differ: a privileged and a standard user, a managed and an unmanaged device where permitted, and accounts owned by different business units. Run tests in approved environments with test identities and non-sensitive data.
Before generating activity, agree on what a successful record must contain. An event appearing somewhere in a console may be insufficient if it lacks the actor, tenant, timestamp, target resource, or action needed for investigation. Record the relevant time zone and retain the source event identifiers where available so the two sides can be matched reliably.
A practical sequence is:
- Establish the baseline. Confirm the integration, granted permissions, enabled audit settings, account scope, and any known exclusions. Check that the independent source is recording the selected activity.
- Generate known actions. Perform specific, authorized actions such as signing in, sharing a test file externally, downloading it, or changing a test resource’s permissions. Record the actor, target, time, and expected outcome.
- Trace each action. Find it in the source audit record and then in the CASB. Compare the event type and fields, not just the total number of events.
- Repeat under different conditions. Test another tenant, account, region, access path, or device category where those differences matter to the deployment.
- Investigate discrepancies. Check whether a missing or incomplete event is caused by source logging, permissions, filtering, ingestion delay, product support, or an incorrect test assumption.
Where a policy or alert is part of the requirement, test that separately from event ingestion. An activity can be visible in a searchable log without producing an alert; conversely, an alert may provide too little context for an analyst to investigate without returning to the source system. Check the actual analyst workflow, including whether the event can be located and interpreted by the people expected to handle it.
Do not treat one successful event as proof of continuous or comprehensive coverage. A small test demonstrates the behavior of the selected events under the tested configuration. Broader confidence requires a representative sample and continued checks after deployment.
How can coverage and delay be measured without overstating the result?
Use the coverage matrix to calculate a result for a defined sample. For example, an event-observation rate can be the number of selected source events correctly matched in the CASB divided by the number of selected source events generated and confirmed in the source records. State the services, event types, accounts, access paths, and observation period included in that denominator.
Report missing events separately from events that arrived with incomplete fields. The latter may be usable for a count but inadequate for an investigation. Also distinguish unsupported activity from activity that should have been collected but was not. Combining those categories into a single percentage can conceal a serious gap in a high-priority workflow.
Measure delay using clearly defined timestamps: when the activity occurred, when the source made its audit record available, and when the CASB made the corresponding event searchable or generated the expected alert. The difference between action time and CASB availability can include delays outside the CASB itself. Compare the observed delay with the response window required for that use case, and record the range observed across the test rather than relying on one fast event.
A successful result for routine file access does not establish equivalent coverage for privileged changes or a newly added tenant. Acceptance criteria should therefore name the priority workflows and minimum required fields, as well as any acceptable exclusions and alternative controls.
Which blind spots should remain on the operating record?
Some gaps are architectural: an application may not expose a required event through its available interface, or an access path may bypass traffic inspection. Others are operational: a connector can lose authorization, a new cloud account may not be enrolled, logging can be disabled, or a license change may affect a feature. Capture each gap with its affected scope, consequence, owner, and compensating source or control.
Pay particular attention to ownership boundaries. A central security team may administer the CASB while individual cloud teams control audit settings and permissions. When an event stops arriving, those teams need an agreed route to determine whether the source stopped producing it, the connector lost access, or the event was filtered downstream. Without that division of responsibility, a dashboard can appear healthy while a specific workflow is unobserved.
Data handling is part of the assessment. Confirm where collected records and inspected content are processed and retained, which administrators can access them, and whether the deployment meets the organization’s applicable privacy and residency requirements. Retention should also be long enough for the investigations the team expects to conduct; a visible event that disappears before it can be examined has limited operational value.
What evidence should be required before acceptance and after deployment?
For a pilot or procurement decision, request a documented mapping between each priority use case and the supported service, integration method, permissions, required license, event fields, and known limitations. Ask the supplier to demonstrate the workflow in the organization’s representative configuration and to explain which results depend on the cloud provider’s own logging or APIs.
Acceptance records should include the test matrix, source-to-CASB matches, observed delays, unresolved gaps, and any assumptions about device routing or account enrollment. Assign remediation dates and owners where a required condition is not met. A supplier’s published support statement can help define the test, but it cannot replace evidence from the relevant tenants and settings.
After acceptance, repeat a smaller set of checks on a scheduled basis and after material changes, such as adding a cloud account, changing connector permissions, or altering a traffic route. Monitor connector health alongside event volumes and perform a known-action test for critical workflows. The operating question remains specific: for the services and identities the organization depends on, can the team still find and use the evidence it expects?
Want to dive deeper into these market dynamics, or need data-driven support for your next business move? Drop a line below and let the analysts at CyberTrade provide customized insights.
Related News
 Identity AccessIs Cloud-Hosted RADIUS a Good Fit for Multicloud Enterprises?Posted on Nov 18, 2026Is a cloud-hosted RADIUS server a good fit for a multicloud enterprise? Explore integration, security, resilience, and costs before you decide.
 Identity AccessHow to Test RADIUS Failover Across Cloud RegionsPosted on Nov 18, 2026How do we test RADIUS failover across cloud regions? Follow a practical guide to verify recovery, secure access, audit logs, and failback.
 Identity AccessHow to Choose a Certificate Authority for Multicloud WorkloadsPosted on Nov 18, 2026How do we choose a certificate authority for workloads across multiple clouds? Explore key criteria, compare CA options, and plan a production-ready pilot.
 Multi-CloudHow to Verify CASB Visibility Across Multiple CloudsPosted on Nov 18, 2026How can we verify a CASB's visibility across multiple clouds? Learn to test coverage, trace events, uncover blind spots, and build a reliable assessment.
 Cloud SecurityHow to Test WAF Attack Blocking Without Disrupting Legitimate TrafficPosted on Nov 18, 2026How do we test whether a WAF blocks attacks without disrupting legitimate traffic? Explore safe simulations, false-positive checks, and staged enforcement.
 Identity AccessCan Smart Cards Work With Cloud Apps Without Replacing Your IdP?Posted on Nov 18, 2026Can smart cards work with cloud applications without replacing our identity system? Discover the integration requirements, security benefits, and pilot checks.
 Prices & CostsHow to Compare Cloud HSM Total Costs Across ProvidersPosted on Nov 18, 2026How do we compare the total cost of cloud HSMs across providers? Discover the hidden charges, key assumptions, and practical steps for a fair comparison.
 Multi-CloudHow to Verify Consistent API Gateway Authentication Across CloudsPosted on Nov 18, 2026Verify API gateway authentication across clouds with practical tests for tokens, routes, bypass risks, and policy enforcement. Explore the guide.
 Cloud SecurityDo You Need a Next-Generation Firewall in Every Cloud?Posted on Nov 18, 2026Do we need a next-generation firewall in every cloud environment? Explore traffic risks, cloud-native controls, costs and deployment options.
 Threat ResponseHow to Tell If a Cloud IDS Is Missing TrafficPosted on Nov 18, 2026How can we tell whether an IDS is missing traffic in a cloud environment? Compare flow evidence, test sensor visibility, and uncover hidden coverage gaps.
 Identity AccessHow to check if a certificate authority is trustedPosted on Nov 18, 2026Certificate Authorities aren't trusted equally everywhere. Learn how to check certificate chains, trust stores, and revocation before choosing a CA.
 Cloud SecurityCan cloud access security brokers detect shadow IT?Posted on Nov 18, 2026Cloud Access Security Brokers can uncover shadow IT—but visibility has limits. Discover how CASBs detect cloud apps, expose blind spots, and guide a practical response.











