
How to check if a certificate authority is trusted
How can you tell whether a certificate authority is trusted in your organization’s environment? The answer depends on more than the issuer’s name: trust can vary by operating system, browser, application, and enterprise policy. Evaluating Certificate Authorities means inspecting certificate chains, identifying the trust store a client actually uses, and checking validity and revocation under real operating conditions.
For a purchasing decision, the useful question is not simply “Is this CA trusted?” It is “Will the intended clients validate the certificates we plan to issue, for the intended purpose, without creating an unacceptable operational dependency?” A browser test on one managed laptop is a starting point, not an acceptance test for an enterprise.
Start with the certificate and the client that must accept it
A CA is trusted in a particular context when a relying application can build an acceptable certification path from the presented certificate to a trust anchor it recognizes. For a TLS connection, the client also needs to accept the server identity and the certificate’s permitted use. A valid chain alone does not establish that the certificate belongs to the hostname being contacted.
Define the test before looking at suppliers. Is the certificate for a public customer-facing website, an internal API, device authentication, or code signing? Which operating systems, application runtimes, containers, appliances, and partner systems must validate it? A CA suitable for an internal service mesh may be a poor choice for a public website if external visitors do not already trust its root.
Record the client version and its management state as well. An enterprise policy can add a private root, remove a public root, or direct traffic through a TLS-inspecting proxy. The issuer seen by a managed workstation may therefore differ from the issuer seen on an unmanaged connection.
Inspect the chain, not just the issuer label
Open the certificate details in the relevant browser or application and inspect the certification path. A typical path contains a leaf certificate, one or more intermediate CA certificates, and a root that the client treats as a trust anchor. The server normally supplies the leaf and required intermediates; the client generally already has the root.
The name displayed beside “Issuer” identifies the certificate that signed a particular certificate. It does not prove that the signing CA is trusted by every client, or even that the server supplied the intermediate needed to build the path. Compare certificate fingerprints when identifying a specific root or intermediate: similar names are not enough to distinguish certificates or cross-signed variants.
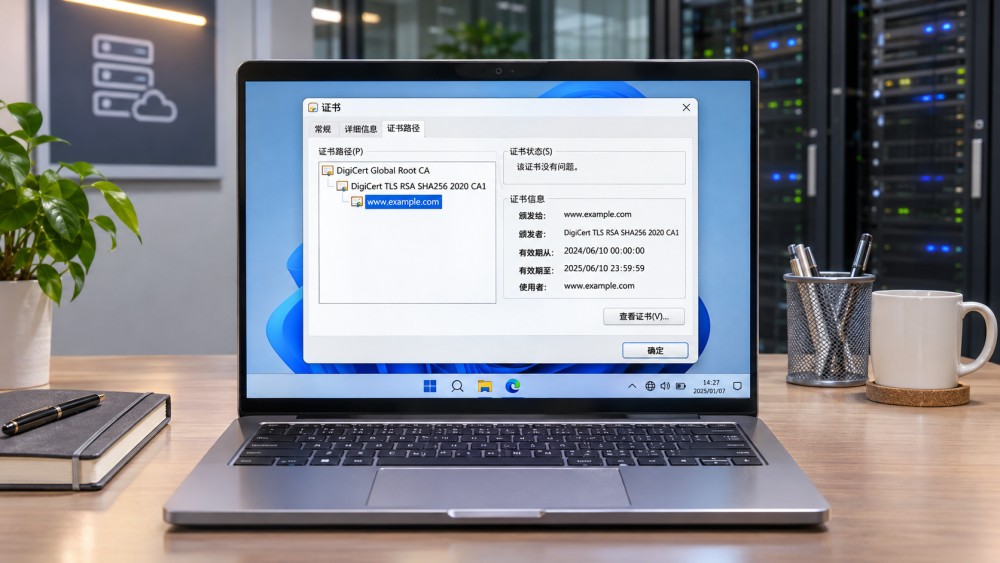
Cross-signing deserves attention during evaluation. A certificate may build to different roots depending on the intermediates available and the client’s path-building behavior. One path can succeed while another fails on an older device. Ask the supplier which chain it intends to serve and test that exact chain on representative clients, especially where legacy appliances or long-lived embedded devices are involved.
Check the leaf certificate’s subject alternative names against the actual DNS name, its validity period, and its extended key usage where applicable. Also examine CA constraints and permitted usages along the path. A certificate issued by a recognized authority can still be rejected because it is expired, intended for a different purpose, or subject to a constraint the application enforces.
Find the trust store that actually decides
There is no single enterprise-wide trust store unless the organization has deliberately built and maintained one. Windows, macOS, Linux distributions, browsers, Java runtimes, containers, and network appliances may use different sources of trust. Some applications use operating-system roots; others use a bundled or separately configured store. Configuration and version matter.
On Windows, certificate management tools can show roots installed for the local machine or a particular user. On Linux, inspect the distribution’s configured CA bundle and update mechanism. For Java applications, check the trust store configured for the running process rather than assuming the host operating system’s store is authoritative. For containers, inspect the image and runtime configuration: updating the host does not necessarily update the image’s CA bundle.
Root presence is evidence of potential trust, not proof of successful validation. A root may have purpose-specific restrictions, an application may apply additional distrust rules, or the chain may fail for another reason. Conversely, an intermediate may be trusted directly by an application or enterprise policy. Document the actual trust anchor selected during the test whenever the client exposes it.
For public CAs, consult the relevant root program’s published documentation as well as the supplier’s compatibility claims. Microsoft, Apple, Mozilla, and browser vendors publish information about their trust programs and certificate policies. Those sources help establish program status, but the deciding evidence is still a validation test using the versions and policies deployed in your environment.
Test the connection from the network that matters
A command-line check can expose the chain presented by a TLS endpoint. For example, with a current OpenSSL installation, an evaluator can use:
openssl s_client -connect example.com:443 -servername example.com -showcerts -verify_return_error -verify_hostname example.com
Replace the hostname and port with the authorized test target. The server name option sends SNI, which matters when an endpoint hosts multiple domains. The command displays certificates supplied by the server and attempts verification using the trust settings available to that OpenSSL installation. Depending on the environment, you may need to specify the intended CA bundle with -CAfile or a certificate directory with -CApath.
Do not treat a successful OpenSSL result as proof that every browser or application will succeed. OpenSSL may use a different trust store and validation behavior, and this command does not by itself establish that the application’s revocation policy has been satisfied. Repeat the test with the real client, from the relevant network segment, using its actual configuration.
If results differ, capture both the peer certificates and the selected path. Common causes include a missing intermediate, a stale container image, a different trust store, hostname mismatch, clock drift, or TLS interception. Avoid “fixing” the problem by disabling certificate validation: that can turn a diagnostic shortcut into a production exposure.
Treat revocation as an operational dependency
An unexpired certificate can still be revoked. Depending on the certificate and client, revocation information may be obtained through a certificate revocation list (CRL), the Online Certificate Status Protocol (OCSP), or a client-specific mechanism. A server may also provide a stapled OCSP response, but clients differ in how they use it.
The crucial question is not just whether a CA publishes revocation information. Determine whether the application checks it, how current the information must be, and what happens when the responder or distribution point is unreachable. Some clients or configurations may continue when status cannot be checked; others may reject the connection. Do not assume uniform behavior across a fleet.
Test from restricted network zones, including workloads without general internet access. Ask whether firewalls, proxies, DNS, or supplier infrastructure are dependencies. For critical systems, agree on the availability trade-off: a strict failure policy can block compromised credentials more reliably in some circumstances, but it can also interrupt legitimate operations when status infrastructure fails. The right setting depends on the client’s capabilities and the service’s risk tolerance.
Public trust and private trust solve different problems
A publicly trusted CA is generally appropriate when unknown external users need to connect without installing an organization-specific root. Public trust does not eliminate deployment work: the team still needs to manage domain validation, certificate issuance, renewal, intermediate chains, and client compatibility.
A private CA can give an organization more control over internal identities and issuance policy. The cost is that trust must be distributed and maintained across every relying client. That includes contractor devices, application runtimes, containers, disaster-recovery systems, and partner integrations—not just domain-joined laptops.
Adding a private root is a significant security decision. Systems that trust it may accept certificates issued beneath it, subject to their validation rules and any effective constraints. Protect the CA’s signing keys, restrict who can request and approve certificates, and establish how the root will be removed or replaced after compromise. Installing a root merely to silence a warning is not a sound acceptance procedure.
Turn supplier claims into acceptance criteria
For a CA selection, request evidence for the exact certificate profile and deployment model under consideration. A generic statement that a provider is “widely trusted” does not identify the root, chain, client versions, or operational conditions behind the claim. A useful evaluation package should include:
- The proposed root and intermediate certificates, fingerprints, chain options, certificate profiles, and intended use.
- Supported issuance and renewal methods, including automation interfaces and ownership of validation steps.
- Revocation procedures, status-service dependencies, incident notification arrangements, and escalation contacts.
- Key protection and administrative controls appropriate to the chosen public or private CA model, supported by current documentation and any relevant independent assessment within its stated scope.
- A transition plan for root changes, intermediate replacement, supplier exit, and emergency reissuance.
Then run a pilot that includes more than a successful initial connection. Issue a test certificate, deploy it through the intended workflow, renew or replace it, and confirm that monitoring detects an approaching expiry. Exercise revocation where practical and observe what representative clients actually do. Include at least one constrained environment if production depends on it, such as an isolated appliance network or a container platform with separately managed images.
Keep the resulting evidence with the decision: test date, client and CA versions, trust-store source, chain fingerprints, network conditions, and observed outcome. This makes a later failure easier to investigate and prevents a point-in-time supplier claim from becoming an assumption about the entire estate. Before approval, assign an owner for root-store updates and certificate lifecycle monitoring; without one, today’s trusted chain can become tomorrow’s outage.
Want to dive deeper into these market dynamics, or need data-driven support for your next business move? Drop a line below and let the analysts at CyberTrade provide customized insights.
Related News
 Identity AccessIs Cloud-Hosted RADIUS a Good Fit for Multicloud Enterprises?Posted on Nov 18, 2026Is a cloud-hosted RADIUS server a good fit for a multicloud enterprise? Explore integration, security, resilience, and costs before you decide.
 Identity AccessHow to Test RADIUS Failover Across Cloud RegionsPosted on Nov 18, 2026How do we test RADIUS failover across cloud regions? Follow a practical guide to verify recovery, secure access, audit logs, and failback.
 Identity AccessHow to Choose a Certificate Authority for Multicloud WorkloadsPosted on Nov 18, 2026How do we choose a certificate authority for workloads across multiple clouds? Explore key criteria, compare CA options, and plan a production-ready pilot.
 Multi-CloudHow to Verify CASB Visibility Across Multiple CloudsPosted on Nov 18, 2026How can we verify a CASB's visibility across multiple clouds? Learn to test coverage, trace events, uncover blind spots, and build a reliable assessment.
 Cloud SecurityHow to Test WAF Attack Blocking Without Disrupting Legitimate TrafficPosted on Nov 18, 2026How do we test whether a WAF blocks attacks without disrupting legitimate traffic? Explore safe simulations, false-positive checks, and staged enforcement.
 Identity AccessCan Smart Cards Work With Cloud Apps Without Replacing Your IdP?Posted on Nov 18, 2026Can smart cards work with cloud applications without replacing our identity system? Discover the integration requirements, security benefits, and pilot checks.
 Prices & CostsHow to Compare Cloud HSM Total Costs Across ProvidersPosted on Nov 18, 2026How do we compare the total cost of cloud HSMs across providers? Discover the hidden charges, key assumptions, and practical steps for a fair comparison.
 Multi-CloudHow to Verify Consistent API Gateway Authentication Across CloudsPosted on Nov 18, 2026Verify API gateway authentication across clouds with practical tests for tokens, routes, bypass risks, and policy enforcement. Explore the guide.
 Cloud SecurityDo You Need a Next-Generation Firewall in Every Cloud?Posted on Nov 18, 2026Do we need a next-generation firewall in every cloud environment? Explore traffic risks, cloud-native controls, costs and deployment options.
 Threat ResponseHow to Tell If a Cloud IDS Is Missing TrafficPosted on Nov 18, 2026How can we tell whether an IDS is missing traffic in a cloud environment? Compare flow evidence, test sensor visibility, and uncover hidden coverage gaps.
 Identity AccessHow to check if a certificate authority is trustedPosted on Nov 18, 2026Certificate Authorities aren't trusted equally everywhere. Learn how to check certificate chains, trust stores, and revocation before choosing a CA.
 Cloud SecurityCan cloud access security brokers detect shadow IT?Posted on Nov 18, 2026Cloud Access Security Brokers can uncover shadow IT—but visibility has limits. Discover how CASBs detect cloud apps, expose blind spots, and guide a practical response.











