
What does FIPS 140-3 mean for hardware security modules?
FIPS 140-3 validates cryptographic modules against defined security requirements. For technical evaluators, its value depends on whether the certificate covers the exact module and operating configuration intended for deployment.
A validated HSM can provide independently assessed evidence for cryptographic controls, but the certificate alone does not establish application security, operational resilience, regulatory compliance, or suitability for a particular workload.
Evaluation therefore starts with the certificate and security policy, then moves to integration, key management, operational procedures, and acceptance testing. The decisive question is whether the validated configuration can support the organization’s actual requirements.
What does FIPS 140-3 validate in an HSM?
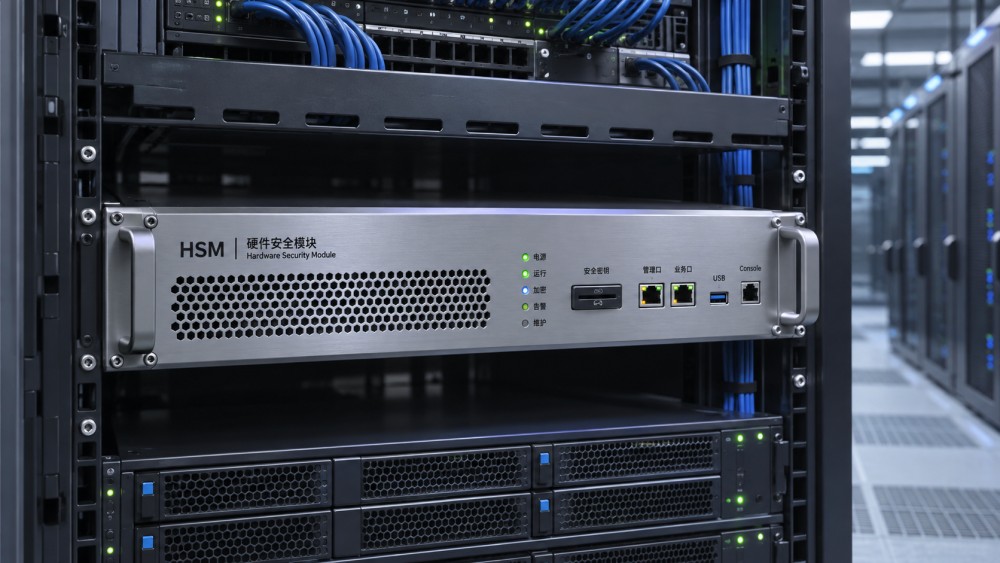
FIPS 140-3 is a United States federal standard for cryptographic modules: hardware, software, firmware, or combinations of these that perform approved cryptographic functions within a defined boundary.
Hardware Security Modules, or HSMs, are commonly evaluated as hardware cryptographic modules. Testing is performed by accredited laboratories, while validation is issued through the Cryptographic Module Validation Program, or CMVP.
The standard specifies requirements across areas including cryptographic interfaces, authentication, physical security, sensitive security parameter management, self-tests, lifecycle assurance, and mitigation of other attacks where applicable.
Validation concerns a particular module and its documented configurations. It should not be interpreted as an endorsement of every product from the supplier or every service built around that module.
For a buyer, the practical outcome is a defined body of evidence: a validation certificate, a published security policy, applicable module documentation, and a set of conditions for approved operation.
Those conditions matter because a device can have the right product name and still fall outside the validated configuration if its firmware, hardware revision, settings, or operating mode differ.
How can you verify a vendor’s FIPS 140-3 claim?
Start with the supplier’s certificate number and find the corresponding entry in the CMVP validated modules database. Check the record directly rather than relying on a product brochure.
Confirm that the certificate identifies FIPS 140-3, the expected module name, the validation status, and the hardware, firmware, or software versions relevant to the proposed deployment.
Then read the linked security policy. It describes the module boundary, security levels, approved services and algorithms, roles, authentication requirements, and conditions needed to operate within the validated configuration.
Ask the supplier to map the exact orderable product, hardware revision, firmware build, and deployment model to that documentation. A product family name alone is not a sufficient match.
Check whether the intended algorithms, key sizes, protocols, and administrative operations are approved services in the specified configuration. A supported function is not necessarily available as an approved service.
Also distinguish a validated module from a module submitted for testing or listed as being in process. Neither an application for validation nor a laboratory engagement is a completed validation.
Review the certificate’s current status and any accompanying notes immediately before purchasing and again before acceptance. Historical or revoked listings may have different implications from active validations.
Finally, establish how the supplier will notify you about firmware changes, validation status changes, and replacements. Record who owns reassessment when the deployed configuration changes.
What do the four security levels mean for procurement?
FIPS 140-3 defines four increasing qualitative security levels. The overall level is useful for screening, but evaluators should inspect individual requirement areas in the certificate and security policy.
Level 1 provides a baseline for cryptographic module security. It does not require the physical security mechanisms associated with higher levels, so deployment environment remains especially important.
Level 2 adds requirements that can include tamper-evident physical security and role-based operator authentication. The actual protections depend on the module type and its documented design.
Level 3 adds stronger physical security requirements and identity-based authentication. Depending on the design and applicable requirements, attempts at physical access can trigger protective actions such as zeroization.
Level 4 provides the highest physical security level under the standard, with more comprehensive protections against physical attacks and environmental conditions. It is not automatically necessary for every workload.
A higher level does not guarantee better throughput, easier integration, stronger authorization in your application, or recovery from an outage. Those properties require separate technical and operational assessment.
Select a target level using threat models, contractual obligations, physical access assumptions, and the sensitivity of protected keys. Verify each relevant security area instead of treating the overall number as a complete comparison.
Does validation cover your deployment and cloud service?
The cryptographic boundary separates the validated module from surrounding components. An application server, management console, network connection, or customer workflow may sit outside that boundary.
In an on-premises deployment, confirm which chassis, cards, firmware, power arrangements, and administrative interfaces are included. Check whether external key backups or client libraries have separate validation claims.
For a managed or cloud HSM, identify the underlying module certificate and ask whether the provider’s offered hardware and firmware match it. A cloud service name is not itself a module certificate.
Request a responsibility matrix covering initialization, approved-mode configuration, administrative access, logging, patching, key backup, disaster recovery, and evidence available to customers. Some activities remain under the provider’s control.
Multitenant architecture and logical partitioning also deserve scrutiny. Determine how the service isolates tenants, who controls administrative credentials, and what evidence supports those claims beyond the module validation.
Where data location or sovereignty matters, document the regions, backup locations, support access, and cross-border dependencies. FIPS validation does not by itself establish residency or jurisdictional compliance.
Which key-management and integration checks matter most?
Map each intended use case, such as certificate authority signing, database encryption, payment processing, or application key protection, to the relevant HSM interfaces and approved services.
Confirm compatibility with existing applications and libraries, including interfaces such as PKCS #11, Java cryptography providers, or vendor APIs where relevant. Interface support does not guarantee application compatibility.
Test the complete key lifecycle: generation, import, use, rotation, backup, restoration, revocation, archival, and destruction. Identify which steps occur inside the validated boundary and which depend on external systems.
Ask how the HSM generates keys and protects them during transport or backup. Verify that wrapping methods, key sizes, and procedures are permitted for the intended approved operation.
Examine administrative separation of duties, authentication methods, quorum controls, and emergency access. Determine whether the security policy requires particular roles or procedures and whether staff can sustain them.
Review audit events for key use, configuration changes, authentication failures, and administrative actions. Test how logs reach monitoring systems and whether they contain enough detail for investigation.
Measure performance with representative algorithms, key sizes, concurrency, network latency, and application behavior. Vendor transaction figures may not predict production throughput or signing latency for your workload.
Exercise failover and restoration using the proposed architecture. An HSM can protect keys effectively while an untested recovery process still leaves critical services unavailable.
What evidence should be included in a procurement evaluation?
Turn the validation claim into a traceable acceptance requirement. Ask suppliers to provide a certificate number, security policy, exact configuration, approved-mode instructions, and documented version mapping.
Request an architecture diagram showing the cryptographic boundary, administrative paths, client connections, backup components, and external dependencies. Mark which components are covered by which independent assessments.
Require a use-case matrix listing each operation, algorithm, key size, interface, and intended mode. Suppliers should identify unsupported operations and any operation outside the approved configuration.
For cloud services, request documentation identifying the provider’s responsibilities and the evidence customers can inspect. Escalate any gap between the advertised service and the certified module configuration.
Set measurable pilot criteria for throughput, latency, availability behavior, administrative workflows, and recovery. Define the workload, observation period, test environment, and pass thresholds before comparing results.
Include lifecycle costs: devices or service charges, partitions, licensing, client integration, redundant capacity, backup infrastructure, training, support, and migration. Confirm how upgrades may affect validation coverage.
Before production acceptance, capture the installed versions and settings, verify approved operation using the supplier’s documented indicators, and retain evidence alongside the configuration baseline and change record.
Does FIPS 140-3 validation make an organization compliant?
No. FIPS 140-3 validates a cryptographic module against specified requirements; it does not certify the security of an organization, application, cloud architecture, or complete business process.
Whether validation is mandatory depends on the applicable jurisdiction, authority, contract, system classification, and effective requirements. United States federal requirements should not be assumed to apply universally.
Some frameworks or contracts may specify an approved module, a minimum security level, particular algorithms, or transition conditions. Obtain the governing requirement and verify its exact language and scope.
Also check the current rules for existing FIPS 140-2 deployments rather than assuming that every older certificate is immediately unusable. Transition and procurement decisions depend on applicable guidance and system requirements.
For authoritative details, consult FIPS 140-3, the CMVP program information, and the security policy associated with the specific certificate.
Bottom line for technical evaluators
FIPS 140-3 is valuable evidence that a defined cryptographic module has met independently assessed requirements. Its relevance depends on matching that evidence to the configuration and services you will actually use.
Shortlist Hardware Security Modules only after checking certificate status, security levels, approved operations, integration, recovery, and ownership responsibilities. Accept a deployment when its documented configuration and tested outcomes meet your requirements.
Want to dive deeper into these market dynamics, or need data-driven support for your next business move? Drop a line below and let the analysts at CyberTrade provide customized insights.
Related News
 Identity AccessIs Cloud-Hosted RADIUS a Good Fit for Multicloud Enterprises?Posted on Nov 18, 2026Is a cloud-hosted RADIUS server a good fit for a multicloud enterprise? Explore integration, security, resilience, and costs before you decide.
 Identity AccessHow to Test RADIUS Failover Across Cloud RegionsPosted on Nov 18, 2026How do we test RADIUS failover across cloud regions? Follow a practical guide to verify recovery, secure access, audit logs, and failback.
 Identity AccessHow to Choose a Certificate Authority for Multicloud WorkloadsPosted on Nov 18, 2026How do we choose a certificate authority for workloads across multiple clouds? Explore key criteria, compare CA options, and plan a production-ready pilot.
 Multi-CloudHow to Verify CASB Visibility Across Multiple CloudsPosted on Nov 18, 2026How can we verify a CASB's visibility across multiple clouds? Learn to test coverage, trace events, uncover blind spots, and build a reliable assessment.
 Cloud SecurityHow to Test WAF Attack Blocking Without Disrupting Legitimate TrafficPosted on Nov 18, 2026How do we test whether a WAF blocks attacks without disrupting legitimate traffic? Explore safe simulations, false-positive checks, and staged enforcement.
 Identity AccessCan Smart Cards Work With Cloud Apps Without Replacing Your IdP?Posted on Nov 18, 2026Can smart cards work with cloud applications without replacing our identity system? Discover the integration requirements, security benefits, and pilot checks.
 Prices & CostsHow to Compare Cloud HSM Total Costs Across ProvidersPosted on Nov 18, 2026How do we compare the total cost of cloud HSMs across providers? Discover the hidden charges, key assumptions, and practical steps for a fair comparison.
 Multi-CloudHow to Verify Consistent API Gateway Authentication Across CloudsPosted on Nov 18, 2026Verify API gateway authentication across clouds with practical tests for tokens, routes, bypass risks, and policy enforcement. Explore the guide.
 Cloud SecurityDo You Need a Next-Generation Firewall in Every Cloud?Posted on Nov 18, 2026Do we need a next-generation firewall in every cloud environment? Explore traffic risks, cloud-native controls, costs and deployment options.
 Threat ResponseHow to Tell If a Cloud IDS Is Missing TrafficPosted on Nov 18, 2026How can we tell whether an IDS is missing traffic in a cloud environment? Compare flow evidence, test sensor visibility, and uncover hidden coverage gaps.
 Identity AccessHow to check if a certificate authority is trustedPosted on Nov 18, 2026Certificate Authorities aren't trusted equally everywhere. Learn how to check certificate chains, trust stores, and revocation before choosing a CA.
 Cloud SecurityCan cloud access security brokers detect shadow IT?Posted on Nov 18, 2026Cloud Access Security Brokers can uncover shadow IT—but visibility has limits. Discover how CASBs detect cloud apps, expose blind spots, and guide a practical response.











