
Private Certificate Authorities vs. Public CAs: When to Use Each
Choose a public certificate authority (CA) when a service must be trusted by browsers or devices that the organization does not administer. Choose a private CA when the organization can control which clients trust it and needs to issue certificates for internal identities or systems. Many environments need both: a public certificate for an external application and private certificates for the connections behind it.
The dividing line is not simply whether a server is on the internet. It is whether every relying party—the browser, application, device or service validating the certificate—can build a valid chain to a trusted root and apply the necessary identity and certificate checks. That trust decision determines how certificates can be deployed, renewed, revoked and recovered.
Start with the relying party, not the server location
A public CA issues certificates that chain to roots included in relevant public trust stores, subject to the policies of those trust programs. For a customer-facing website, that pre-established trust avoids asking visitors to install an organization-specific root certificate. A valid chain is still only one part of successful validation: the certificate must also match the requested hostname, be within its validity period and satisfy the client’s other checks.
A private CA issues certificates under a trust hierarchy controlled for a defined environment. Its root or another appropriate trust anchor must be installed or configured in each validating client. This can work well for managed laptops, servers, containers, appliances and devices that can be provisioned through an established administrative channel. It is less suitable when clients are unknown or cannot be configured.
A hostname being internal does not automatically require a private CA. A public certificate can be appropriate for an internally hosted service using an eligible domain name, provided the CA can validate control of that name and issuance meets applicable rules. Conversely, an internet-reachable service can use a private certificate if access is restricted to clients that have been deliberately configured to trust the private hierarchy. Network exposure and trust scope are separate decisions.
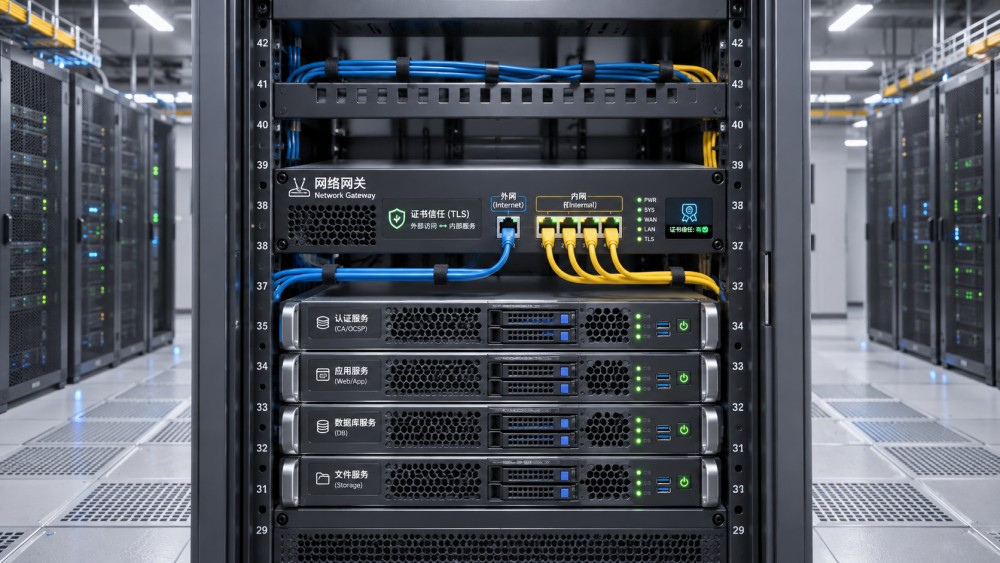
Before selecting a CA, map each connection in the application path. A browser may connect to a public-facing load balancer, which then connects to an application server, which authenticates to a database. Each connection has its own server identity, client population and trust configuration. A single application can therefore have a legitimate need for several certificate types and more than one CA.
Where public CA certificates fit
Public certificates are the natural choice for websites, APIs and other endpoints accessed by external users or third-party software where installing a private root is impractical. They are also useful for internal web applications accessed from unmanaged devices, because clients can validate the server without receiving an enterprise trust anchor.
The operational advantage is interoperability, not an exemption from certificate management. The organization still needs to prove control of the domain, obtain and install certificates, protect private keys, renew certificates before expiry and replace them after a compromise or a CA-directed revocation. Public trust programs impose issuance and lifecycle requirements that can change, so automation should not rely on a fixed assumption about certificate lifetimes.
Domain validation also creates a security dependency. If DNS-based validation is automated, access to the relevant DNS records or delegated validation mechanism must be protected. If an HTTP-based method is used, the CA must be able to reach the required endpoint. Network architecture, DNS ownership and responsibility for the domain all affect whether issuance and renewal can run without manual intervention.
Publicly trusted TLS certificates also have identity constraints. For example, publicly trusted certificates are not a general solution for arbitrary internal-only hostnames. Publicly trusted TLS certificates are normally recorded in Certificate Transparency logs, so the names included may be visible through those logs. Where disclosing an internal naming scheme is a concern, consider the naming architecture and applicable transparency requirements before choosing public issuance.
Where private certificate authorities fit
A private CA is appropriate when the validating systems can be configured to trust it and the organization needs control over issuance policies or identities. Examples include mutual TLS between internal services, authentication of managed devices, internal server certificates and certificates for equipment using names that are not eligible for public issuance.
Private issuance is especially useful when certificate subjects and authorization need to follow an internal identity model. A workload certificate might identify a service rather than a public DNS name; a device certificate might be tied to an asset enrollment process. The value comes from connecting certificate issuance to a reliable source of identity and limiting what each requester can obtain. A private CA that signs any requested identity without adequate authorization provides little assurance about who holds the resulting key.
Control has a cost. Private PKI operators must maintain the CA hierarchy, protect signing keys, define issuance profiles, distribute trust anchors and provide a way to replace certificates or remove trust when necessary. A managed private CA service can operate parts of that infrastructure, but it does not eliminate responsibility for enrollment authorization, client trust distribution, application configuration or incident response.
Private does not mean automatically more secure, and public does not mean the application’s traffic is publicly readable. Both approaches can support encrypted TLS connections. Security depends on key protection, identity validation, certificate policy and the behavior of the clients that validate the chain.
Trust distribution is the practical boundary
The most consequential private-PKI question is whether every relevant client can receive, maintain and eventually remove the trust anchor. Managed operating systems may accept enterprise roots through device management or directory policy, but an application can use a separate trust store. Containers may carry a CA bundle in their image; a Java application may use its own keystore; an appliance may require manual import. Updating the operating system alone does not prove that all clients will trust the new CA.
External partners make the boundary harder. A private certificate can be workable for a partner API when both parties agree on trust distribution, rotation and support procedures. It is a poor fit if each partner’s customers or unmanaged devices must independently install a root. The number of relying parties matters less than the organization’s ability to configure them reliably.
Plan for removal as well as installation. If a private root is compromised, every client that trusts it may accept fraudulent certificates issued under that root unless other controls prevent it. Removing the root, distributing a replacement and reissuing affected certificates can be a large coordinated change. Restricting trust to applications that need it, using appropriately scoped issuing intermediates and protecting root keys reduces exposure, although these measures do not remove the need for a recovery plan.
Evaluate the certificate lifecycle, not just issuance
A CA is only one component of a working certificate system. An evaluation should trace what happens from a request for a certificate through its retirement, including failure conditions.
Enrollment and authorization. Identify how a requester proves its identity and who authorizes the names or identities in the certificate. Check support for relevant enrollment interfaces, such as ACME, EST or SCEP, where those protocols are needed. Protocol support alone is insufficient: test how credentials are issued, scoped, rotated and revoked, and whether an attacker controlling one workload could request a certificate for another.
Renewal and deployment. Verify that automation reaches the actual termination point, not merely that the CA can issue a renewed certificate. A load balancer, application process or appliance may need a reload or an API update before it presents the new certificate. Test renewal with the real key storage method, permissions and deployment pipeline, including an expired credential or unavailable CA endpoint.
Key custody. Determine where keys are generated, whether they can be exported and which administrators or services can access them. A CA signing key has a different risk profile from an individual server key. Consider hardware security module support where required, separation of administrative roles and the procedure for replacing a compromised key. Non-exportable keys can reduce exposure but may constrain migration and disaster recovery.
Revocation and enforcement. A CA’s ability to publish a certificate revocation list or provide an OCSP response does not mean every client checks it. Some clients handle an unreachable responder differently; others may not perform the check for a particular connection. Test the actual application and failure mode. Short-lived certificates can reduce the time an exposed certificate remains valid, but they increase dependence on reliable automated renewal and do not replace a compromise response.
Inventory and ownership. Record certificates issued outside the primary automation path as well as those issued by the preferred CA. An inventory is useful only if it identifies the service owner, location of the private key, expiry date, renewal method and dependencies. Without an accountable owner, an alert about an expiring certificate may not translate into a successful replacement.
Architect the CA hierarchy around failure and scope
A private deployment should distinguish the root of trust from the issuing layer. An offline root with one or more issuing intermediates can limit routine exposure of the root signing key. Separate intermediates or issuance profiles can also enforce different policies for server, client and device identities. The precise design depends on the clients and operational requirements: every additional hierarchy or policy boundary introduces administration, monitoring and recovery work.
Check whether clients can build the chain presented by the server and whether they support the chosen algorithms, key sizes and certificate extensions. Older devices may have limitations that conflict with the preferred security profile. A design is not ready merely because a modern browser accepts a test certificate; it must work across the actual population of clients without disabling essential validation.
CA availability also needs to match the application’s certificate lifetime and deployment model. If a service uses short-lived credentials, an enrollment outage can become an application outage once existing certificates expire. Test backup, restoration, audit logging and recovery procedures, including how the organization regains administrative access. For managed services, establish which responsibilities remain with the provider and which remain with the organization.
Use a mixed model where the trust paths differ
Consider an application with a public web interface and an internal application tier. A public CA certificate on the external endpoint allows ordinary browsers to validate the site. A private CA can issue certificates for mutual TLS between the gateway and backend services, where both sides are managed and a private trust bundle can be deployed. The public certificate does not automatically authenticate backend workloads, and the private certificate does not give external browsers public trust.
The same distinction applies to an internal portal accessed by contractors. If contractors use unmanaged devices, a public certificate for an eligible domain can simplify server authentication. If access requires client certificates, the organization must separately decide how those certificates are issued, protected and revoked, and whether the portal supports the chosen client-authentication model.
Before committing to either approach, run a representative pilot across the least flexible clients and the complete renewal path. Acceptance should include successful validation, rejection of an untrusted or mismatched certificate, renewal without manual intervention where required, and a tested response to key compromise. The strongest choice is the one whose trust assumptions and recovery procedures remain workable across the systems that actually depend on it.
Want to dive deeper into these market dynamics, or need data-driven support for your next business move? Drop a line below and let the analysts at CyberTrade provide customized insights.
Related News
 Identity AccessIs Cloud-Hosted RADIUS a Good Fit for Multicloud Enterprises?Posted on Nov 18, 2026Is a cloud-hosted RADIUS server a good fit for a multicloud enterprise? Explore integration, security, resilience, and costs before you decide.
 Identity AccessHow to Test RADIUS Failover Across Cloud RegionsPosted on Nov 18, 2026How do we test RADIUS failover across cloud regions? Follow a practical guide to verify recovery, secure access, audit logs, and failback.
 Identity AccessHow to Choose a Certificate Authority for Multicloud WorkloadsPosted on Nov 18, 2026How do we choose a certificate authority for workloads across multiple clouds? Explore key criteria, compare CA options, and plan a production-ready pilot.
 Multi-CloudHow to Verify CASB Visibility Across Multiple CloudsPosted on Nov 18, 2026How can we verify a CASB's visibility across multiple clouds? Learn to test coverage, trace events, uncover blind spots, and build a reliable assessment.
 Cloud SecurityHow to Test WAF Attack Blocking Without Disrupting Legitimate TrafficPosted on Nov 18, 2026How do we test whether a WAF blocks attacks without disrupting legitimate traffic? Explore safe simulations, false-positive checks, and staged enforcement.
 Identity AccessCan Smart Cards Work With Cloud Apps Without Replacing Your IdP?Posted on Nov 18, 2026Can smart cards work with cloud applications without replacing our identity system? Discover the integration requirements, security benefits, and pilot checks.
 Prices & CostsHow to Compare Cloud HSM Total Costs Across ProvidersPosted on Nov 18, 2026How do we compare the total cost of cloud HSMs across providers? Discover the hidden charges, key assumptions, and practical steps for a fair comparison.
 Multi-CloudHow to Verify Consistent API Gateway Authentication Across CloudsPosted on Nov 18, 2026Verify API gateway authentication across clouds with practical tests for tokens, routes, bypass risks, and policy enforcement. Explore the guide.
 Cloud SecurityDo You Need a Next-Generation Firewall in Every Cloud?Posted on Nov 18, 2026Do we need a next-generation firewall in every cloud environment? Explore traffic risks, cloud-native controls, costs and deployment options.
 Threat ResponseHow to Tell If a Cloud IDS Is Missing TrafficPosted on Nov 18, 2026How can we tell whether an IDS is missing traffic in a cloud environment? Compare flow evidence, test sensor visibility, and uncover hidden coverage gaps.
 Identity AccessHow to check if a certificate authority is trustedPosted on Nov 18, 2026Certificate Authorities aren't trusted equally everywhere. Learn how to check certificate chains, trust stores, and revocation before choosing a CA.
 Cloud SecurityCan cloud access security brokers detect shadow IT?Posted on Nov 18, 2026Cloud Access Security Brokers can uncover shadow IT—but visibility has limits. Discover how CASBs detect cloud apps, expose blind spots, and guide a practical response.











