
FIDO2 Security Keys: A Practical Guide to Phishing-Resistant Login
FIDO2 security keys offer a practical way to strengthen login security against phishing, but their effectiveness depends on how they are deployed and supported.
For organizations evaluating passwordless or multifactor authentication, compatibility, enrollment, lost-key recovery, and administration matter as much as the technology. This guide explains how to assess them.
The overall judgment: security keys can provide strong phishing resistance, but only when applications, fallback methods, and help-desk processes support the same security objective.
What Are FIDO2 Security Keys, and How Do They Stop Phishing?
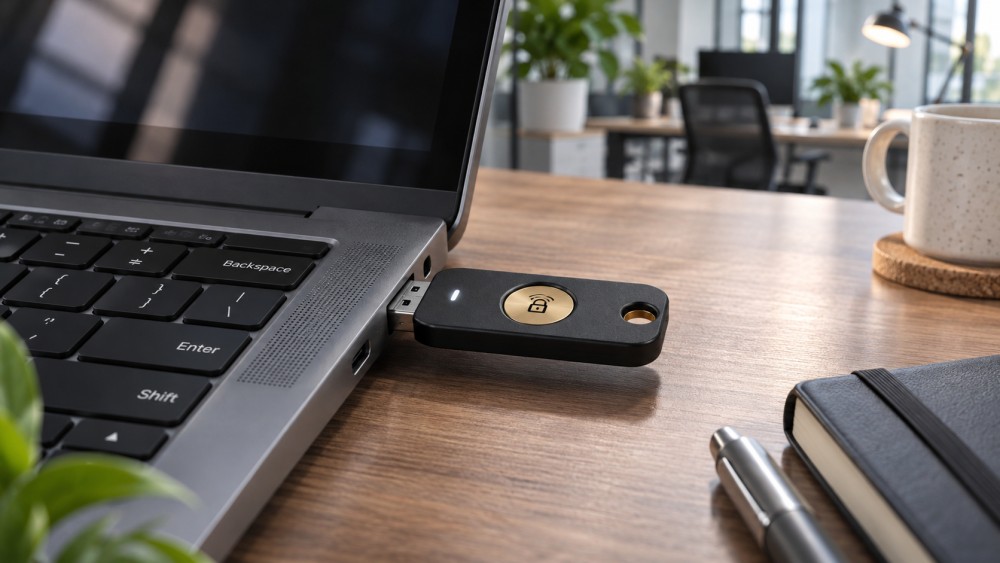
A FIDO2 security key is a physical authenticator that supports public-key authentication through compatible browsers, operating systems, and applications or identity providers.
During registration, the authenticator creates a private key and a corresponding public key. The service stores the public key; the private key remains protected by the authenticator.
At login, the service sends a challenge. The authenticator signs it after the required user action, and the service verifies the signature using the registered public key.
Crucially, WebAuthn credentials are bound to the legitimate service’s origin. A convincing phishing site at another domain cannot simply use that credential to authenticate as the real site.
FIDO2 combines Web Authentication, or WebAuthn, with the Client to Authenticator Protocol, commonly called CTAP. WebAuthn connects applications to authenticators; CTAP supports communication with external authenticators.
A security key may connect through USB or NFC, depending on the model and device. Users typically touch it and may also enter a PIN or provide a biometric.
The PIN or biometric, when required for user verification, unlocks use of the credential locally. The biometric itself is not sent to the website as the authentication secret.
FIDO2 can support passwordless login or serve as an additional factor. Whether a particular sign-in qualifies as multifactor depends on authenticator capabilities, configuration, and user verification.
What Risks Do Security Keys Address, and What Do They Leave Open?
Security keys are designed to resist credential phishing and real-time interception of login prompts. Unlike passwords or one-time codes, their authentication response is tied to the legitimate origin.
They also reduce reliance on shared secrets stored by services. A stolen public key alone is not a reusable password for signing in to that account.
These protections do not make an account immune to every attack. Malware on an unlocked device, stolen session cookies, and compromised applications can still undermine an authenticated session.
Attackers may also target registration or recovery. If a help desk resets an account after weak identity checks, a strong key cannot compensate for that alternate path.
Federated sign-in adds another boundary: the key protects authentication at the identity provider, while application sessions and administrative controls still need independent protection.
Organizations should therefore evaluate phishing resistance across the complete login and recovery journey, not merely confirm that a key can be registered.
Where Do FIDO2 Security Keys Fit Best?
Start with users whose accounts provide broad access or are frequent targets: identity administrators, cloud administrators, executives, and staff handling sensitive financial or operational changes.
Keys can also suit employees who move between managed workstations, contractors using compatible devices, and organizations that prefer a separate physical authenticator.
Shared workstations require extra planning. Test browser sessions, user switching, port access, PIN entry, and sign-out behavior before assuming a key-based workflow will scale.
In critical infrastructure or other availability-sensitive environments, test authentication during maintenance windows and establish approved offline or emergency procedures for systems that cannot use modern sign-in.
Some applications may only support older protocols, local accounts, or vendor-specific authentication. Treat those as separate migration or exception decisions rather than assuming universal coverage.
Are Security Keys the Same as Passkeys?
A passkey is a FIDO credential used for passwordless authentication. It may be stored on a physical security key or on a compatible user device.
Device-stored passkeys can be synchronized through an ecosystem provider, while some credentials remain device-bound. The available behavior depends on the authenticator, platform, and organization’s policies.
Physical keys provide a portable, separate authenticator and can help organizations issue and account for dedicated hardware. They also introduce purchasing, distribution, and replacement work.
Synced passkeys can reduce dependence on a separate object, but administrators should examine synchronization, account recovery, device management, and cross-platform access before approving them.
Neither approach is automatically right for every workforce. Compare both against the same application, recovery, user-verification, and audit requirements, then allow combinations where policy permits.
How Can You Check Application and Device Compatibility?
Begin with an inventory of sign-in paths, not just applications. Include browser access, mobile apps, desktop clients, privileged consoles, remote access, and federation through identity providers.
For each path, determine whether FIDO2 authentication is supported directly or through federation, and whether the desired policy requires a particular license or configuration.
Test representative operating systems, browser versions, mobile devices, and key interfaces. A device with USB-C alone, for example, cannot use a USB-A-only key without an adapter.
Check whether mobile workflows support NFC or another appropriate connection, and whether protective cases, accessibility needs, or managed-device restrictions interfere with everyday use.
Verify user verification, conditional access, session duration, and step-up authentication in the actual configuration. Product support statements do not prove that every combination works.
Record exceptions with an owner, affected users, compensating controls, and a review date. Prioritize alternatives that preserve phishing resistance where the environment supports them.
For nonhuman identities and service accounts, investigate workload identity and credential-management controls separately. Physical user keys are generally not a substitute for machine authentication design.
What Should Buyers Compare Before Purchasing?
Choose interfaces based on the actual device fleet: USB-A, USB-C, NFC, or combinations. Confirm connector durability and suitability for frequently used or shared equipment.
Review supported FIDO2 features, PIN and biometric options, credential capacity, and any relevant certification claims. Ask the supplier to identify the exact model and firmware assessed.
Certification can provide useful assurance about a defined product and assessment scope, but it does not demonstrate that the organization’s enrollment, recovery, or application settings are secure.
Ask whether the identity provider can restrict authenticator types and whether device attestation is supported, required, and operationally manageable. Consider privacy and exception implications.
Confirm procurement lead times, regional availability, accessibility accommodations, warranty terms, and replacement processes. A suitable key that cannot be supplied reliably creates an operational dependency.
Consider the full cost: primary and backup keys, shipping, inventory, integration, testing, support training, replacements, and the time users spend enrolling.
Request a pilot using your own applications and representative devices. Define acceptance criteria before testing, including recovery, administrative reporting, and accessibility, not just successful login.
How Should an Enterprise Roll Out Security Keys?
First, assign ownership across identity engineering, security operations, procurement, help desk, and business teams. Decide who approves exceptions and who maintains authentication policies.
Next, document the existing authentication baseline. Identify password resets, phishing-resistant coverage, high-risk accounts, application dependencies, and support workload using definitions your organization can reproduce.
Run a pilot with a diverse group, including administrators, mobile users, remote workers, and users with accessibility requirements. Include common and less common devices.
Test enrollment from a trusted session, registration of backup authenticators, ordinary sign-in, device replacement, and account recovery. Capture failures alongside successful outcomes.
Issue keys through a controlled process that links each device to the intended user without recording sensitive PINs. Provide clear instructions for registration and safe storage.
Where policy and platform support allow, register at least two independent authenticators. Store the backup separately and test that it works before relying on it.
Expand in stages after resolving pilot issues. Communicate upcoming policy changes, support channels, and deadlines, while maintaining approved exceptions for genuinely incompatible workflows.
Finally, monitor enrollment and authentication events, review exceptions, and remove credentials when users leave or keys are lost. Reassess coverage when applications or policies change.
What Happens When a Key Is Lost or a User Is Locked Out?
A lost key should be reported promptly so administrators or users can revoke its registered credential according to policy. Investigate suspected theft or misuse where appropriate.
A registered backup authenticator can restore access without weakening the process, provided it is available and protected. Test this scenario before deployment, not during an incident.
When no backup exists, recovery becomes an identity-proofing decision. Define acceptable evidence, independent verification, approval authority, and logging before the help desk receives its first request.
Avoid treating an easily phished email link or an unverified phone call as equivalent to the original security key. Recovery can otherwise become the attacker’s preferred route.
Temporary access should be narrowly scoped and time-limited where possible. Require the user to register a replacement authenticator and close the temporary path afterward.
Emergency administrator accounts need separate governance, protected credentials, monitoring, and periodic access exercises. Their availability requirements do not eliminate the need for strong controls.
How Do You Measure Whether the Deployment Works?
Track the percentage of in-scope users with a registered phishing-resistant authenticator, using the eligible user population and a stated reporting date as the denominator.
Measure protected sign-in coverage separately. An enrolled user may still access important applications through passwords, weaker fallback methods, or an unprotected legacy client.
Review registration failures, help-desk contacts, recovery completion time, lost-key replacements, and exception age. Segment results by application, device type, and user group where useful.
Define each metric before comparing periods: for example, state whether recovery time begins at the user’s report or at ticket creation, and when it ends.
Use controlled phishing exercises and incident reviews as supporting evidence, while recognizing their scope. A successful test does not prove resistance to session theft or compromised endpoints.
For supplier acceptance, retain test configurations, platform versions, pass and fail criteria, unresolved defects, and responsible owners. Repeat critical tests after material platform changes.
Frequently Asked Questions
Do FIDO2 security keys eliminate passwords?
They can enable passwordless sign-in when the application and policy support it. Passwords may still exist for other applications, recovery, or approved legacy exceptions.
Can a stolen security key be used immediately?
That depends on the credential, required user verification, and account policy. A PIN or biometric can add protection, but a lost key should still be revoked promptly.
Does every employee need two physical keys?
Not necessarily. Two independent authenticators can improve resilience, but the right backup may be another approved FIDO authenticator, subject to organizational policy and platform support.
Are all FIDO2 deployments phishing-resistant?
The FIDO authentication ceremony is designed for phishing resistance, but an account may remain vulnerable if weaker alternate login, enrollment, or recovery routes are available.
Conclusion: Evaluate the Whole Authentication Journey
FIDO2 security keys are a strong option for phishing-resistant login, particularly for privileged and high-risk users. Their value depends on compatible applications and correctly configured policies.
Before scaling, verify real sign-in paths, test independent backups, secure recovery, and budget for ongoing support. Evidence from those checks matters more than a feature checkbox.
For technical background, consult the W3C WebAuthn specification and the FIDO Alliance specifications, then validate their application in your own environment.
Want to dive deeper into these market dynamics, or need data-driven support for your next business move? Drop a line below and let the analysts at CyberTrade provide customized insights.
Related News
 Identity AccessIs Cloud-Hosted RADIUS a Good Fit for Multicloud Enterprises?Posted on Nov 18, 2026Is a cloud-hosted RADIUS server a good fit for a multicloud enterprise? Explore integration, security, resilience, and costs before you decide.
 Identity AccessHow to Test RADIUS Failover Across Cloud RegionsPosted on Nov 18, 2026How do we test RADIUS failover across cloud regions? Follow a practical guide to verify recovery, secure access, audit logs, and failback.
 Identity AccessHow to Choose a Certificate Authority for Multicloud WorkloadsPosted on Nov 18, 2026How do we choose a certificate authority for workloads across multiple clouds? Explore key criteria, compare CA options, and plan a production-ready pilot.
 Multi-CloudHow to Verify CASB Visibility Across Multiple CloudsPosted on Nov 18, 2026How can we verify a CASB's visibility across multiple clouds? Learn to test coverage, trace events, uncover blind spots, and build a reliable assessment.
 Cloud SecurityHow to Test WAF Attack Blocking Without Disrupting Legitimate TrafficPosted on Nov 18, 2026How do we test whether a WAF blocks attacks without disrupting legitimate traffic? Explore safe simulations, false-positive checks, and staged enforcement.
 Identity AccessCan Smart Cards Work With Cloud Apps Without Replacing Your IdP?Posted on Nov 18, 2026Can smart cards work with cloud applications without replacing our identity system? Discover the integration requirements, security benefits, and pilot checks.
 Prices & CostsHow to Compare Cloud HSM Total Costs Across ProvidersPosted on Nov 18, 2026How do we compare the total cost of cloud HSMs across providers? Discover the hidden charges, key assumptions, and practical steps for a fair comparison.
 Multi-CloudHow to Verify Consistent API Gateway Authentication Across CloudsPosted on Nov 18, 2026Verify API gateway authentication across clouds with practical tests for tokens, routes, bypass risks, and policy enforcement. Explore the guide.
 Cloud SecurityDo You Need a Next-Generation Firewall in Every Cloud?Posted on Nov 18, 2026Do we need a next-generation firewall in every cloud environment? Explore traffic risks, cloud-native controls, costs and deployment options.
 Threat ResponseHow to Tell If a Cloud IDS Is Missing TrafficPosted on Nov 18, 2026How can we tell whether an IDS is missing traffic in a cloud environment? Compare flow evidence, test sensor visibility, and uncover hidden coverage gaps.
 Identity AccessHow to check if a certificate authority is trustedPosted on Nov 18, 2026Certificate Authorities aren't trusted equally everywhere. Learn how to check certificate chains, trust stores, and revocation before choosing a CA.
 Cloud SecurityCan cloud access security brokers detect shadow IT?Posted on Nov 18, 2026Cloud Access Security Brokers can uncover shadow IT—but visibility has limits. Discover how CASBs detect cloud apps, expose blind spots, and guide a practical response.











